Arx Cloud vs. Tailscale & NordVPN:
One App Instead of Two VPNs
If all you need is to connect your own computers together for free, Tailscale is great, so use it. NordVPN hides your location but can't reach your home or office network. Arx Cloud does both in one app, and also blocks known bad websites and keeps video calls from lagging. It works on hotel and airport Wifi because it looks like normal web traffic.
Side-by-Side: Arx Cloud vs. Tailscale vs. NordVPN
Why juggle conflicting TUN adapters on your phone and laptop when one security cloud handles your home network access, global exit nodes, firewall steering, and DNS filtering?
| Capability / Architecture | Arx Cloud (Basic / Pro / Prime) | Tailscale / ZeroTier (Mesh-Only) | NordVPN / Mullvad (Consumer Exit VPN) |
|---|---|---|---|
| Core Architecture | Personal & SOHO SASE Cloud (Firewall + Mesh + Exit + DLP) | Flat L3 mesh pipe between devices | Shared public exit VPN tunnel |
| 12 Global Dual-Stack (IPv4/IPv6) Exit PoPs | Included on all plans ($4.99/mo+) | Paid Mullvad add-on ($5/mo per 5 devices) or BYO VPS | Included |
| Zero-Port Home LAN & Proxmox Subnet Relay | Included in Arx Pro ($8.99/mo) & up | Included (Subnet router) | Not supported (Cannot route into home RFC1918 LAN) |
| Single-Pass Cloud Firewall & First-Match L7 Steering | Included (0ms Direct Breakout for Netflix/Zoom + BYO Proxy) | ACLs only (No L7 domain steering or proxy chaining) | All-or-nothing tunnel (App split-tunnel only on select OS) |
| Cloaked Port :443 Transport (Zero Non-443 Exposure) | Always-On QUIC UDP :443 + Stealth TLS 1.3 TCP :443 | Direct UDP or bandwidth-limited DERP relay | Often blocked or throttled on hotel & airline Wifi |
| In-Line AI Prompt & Web Secret Sanitizer (DLP) | Included (Blocks API keys & secrets on ChatGPT / Claude) | Not supported | Not supported |
| Ed25519-Signed Threat Cloud DNS (278,000+ Domains) | Included (Hourly signed feeds + Custom allow/block lists) | Requires external NextDNS / Pi-hole setup | Basic blocklist (No custom per-tenant domain rules) |
Stateless 1:1 CGNAT Overlap Translation (192.168.1.0/24) |
Built-in (Maps colliding subnets into 100.64.x.0/24) |
Manual 4via6 configuration required | Not supported |
| Bring-Your-Own (BYO) SOCKS5 / External Exit Chaining | Included (Route specific rules through NordVPN/Mullvad/VPS) | Not supported | Single provider only |
| Client-Side Private Key Ownership | Enforced (Browser WebCrypto / local keygen; server never sees key) | Client-generated | Often server-provisioned |
| Team Upgrade Path: Arx Private Access | Business Team ($10/seat/mo): Arx Private Access with app-by-app access, device checks & private internal names | Peer/subnet ACLs only (No in-line DLP, SAML proxy, or vaulted MCP broker) | Separate NordLayer B2B product |
Already Have NordVPN or Mullvad? Chain It Inside Arx Cloud
You don't even have to throw away an existing proxy subscription. Add your SOCKS5 or external exit credentials under BYO Proxies in the Arx Console and steer specific domains through it while keeping your home or office LAN relay and Threat Cloud DNS active.
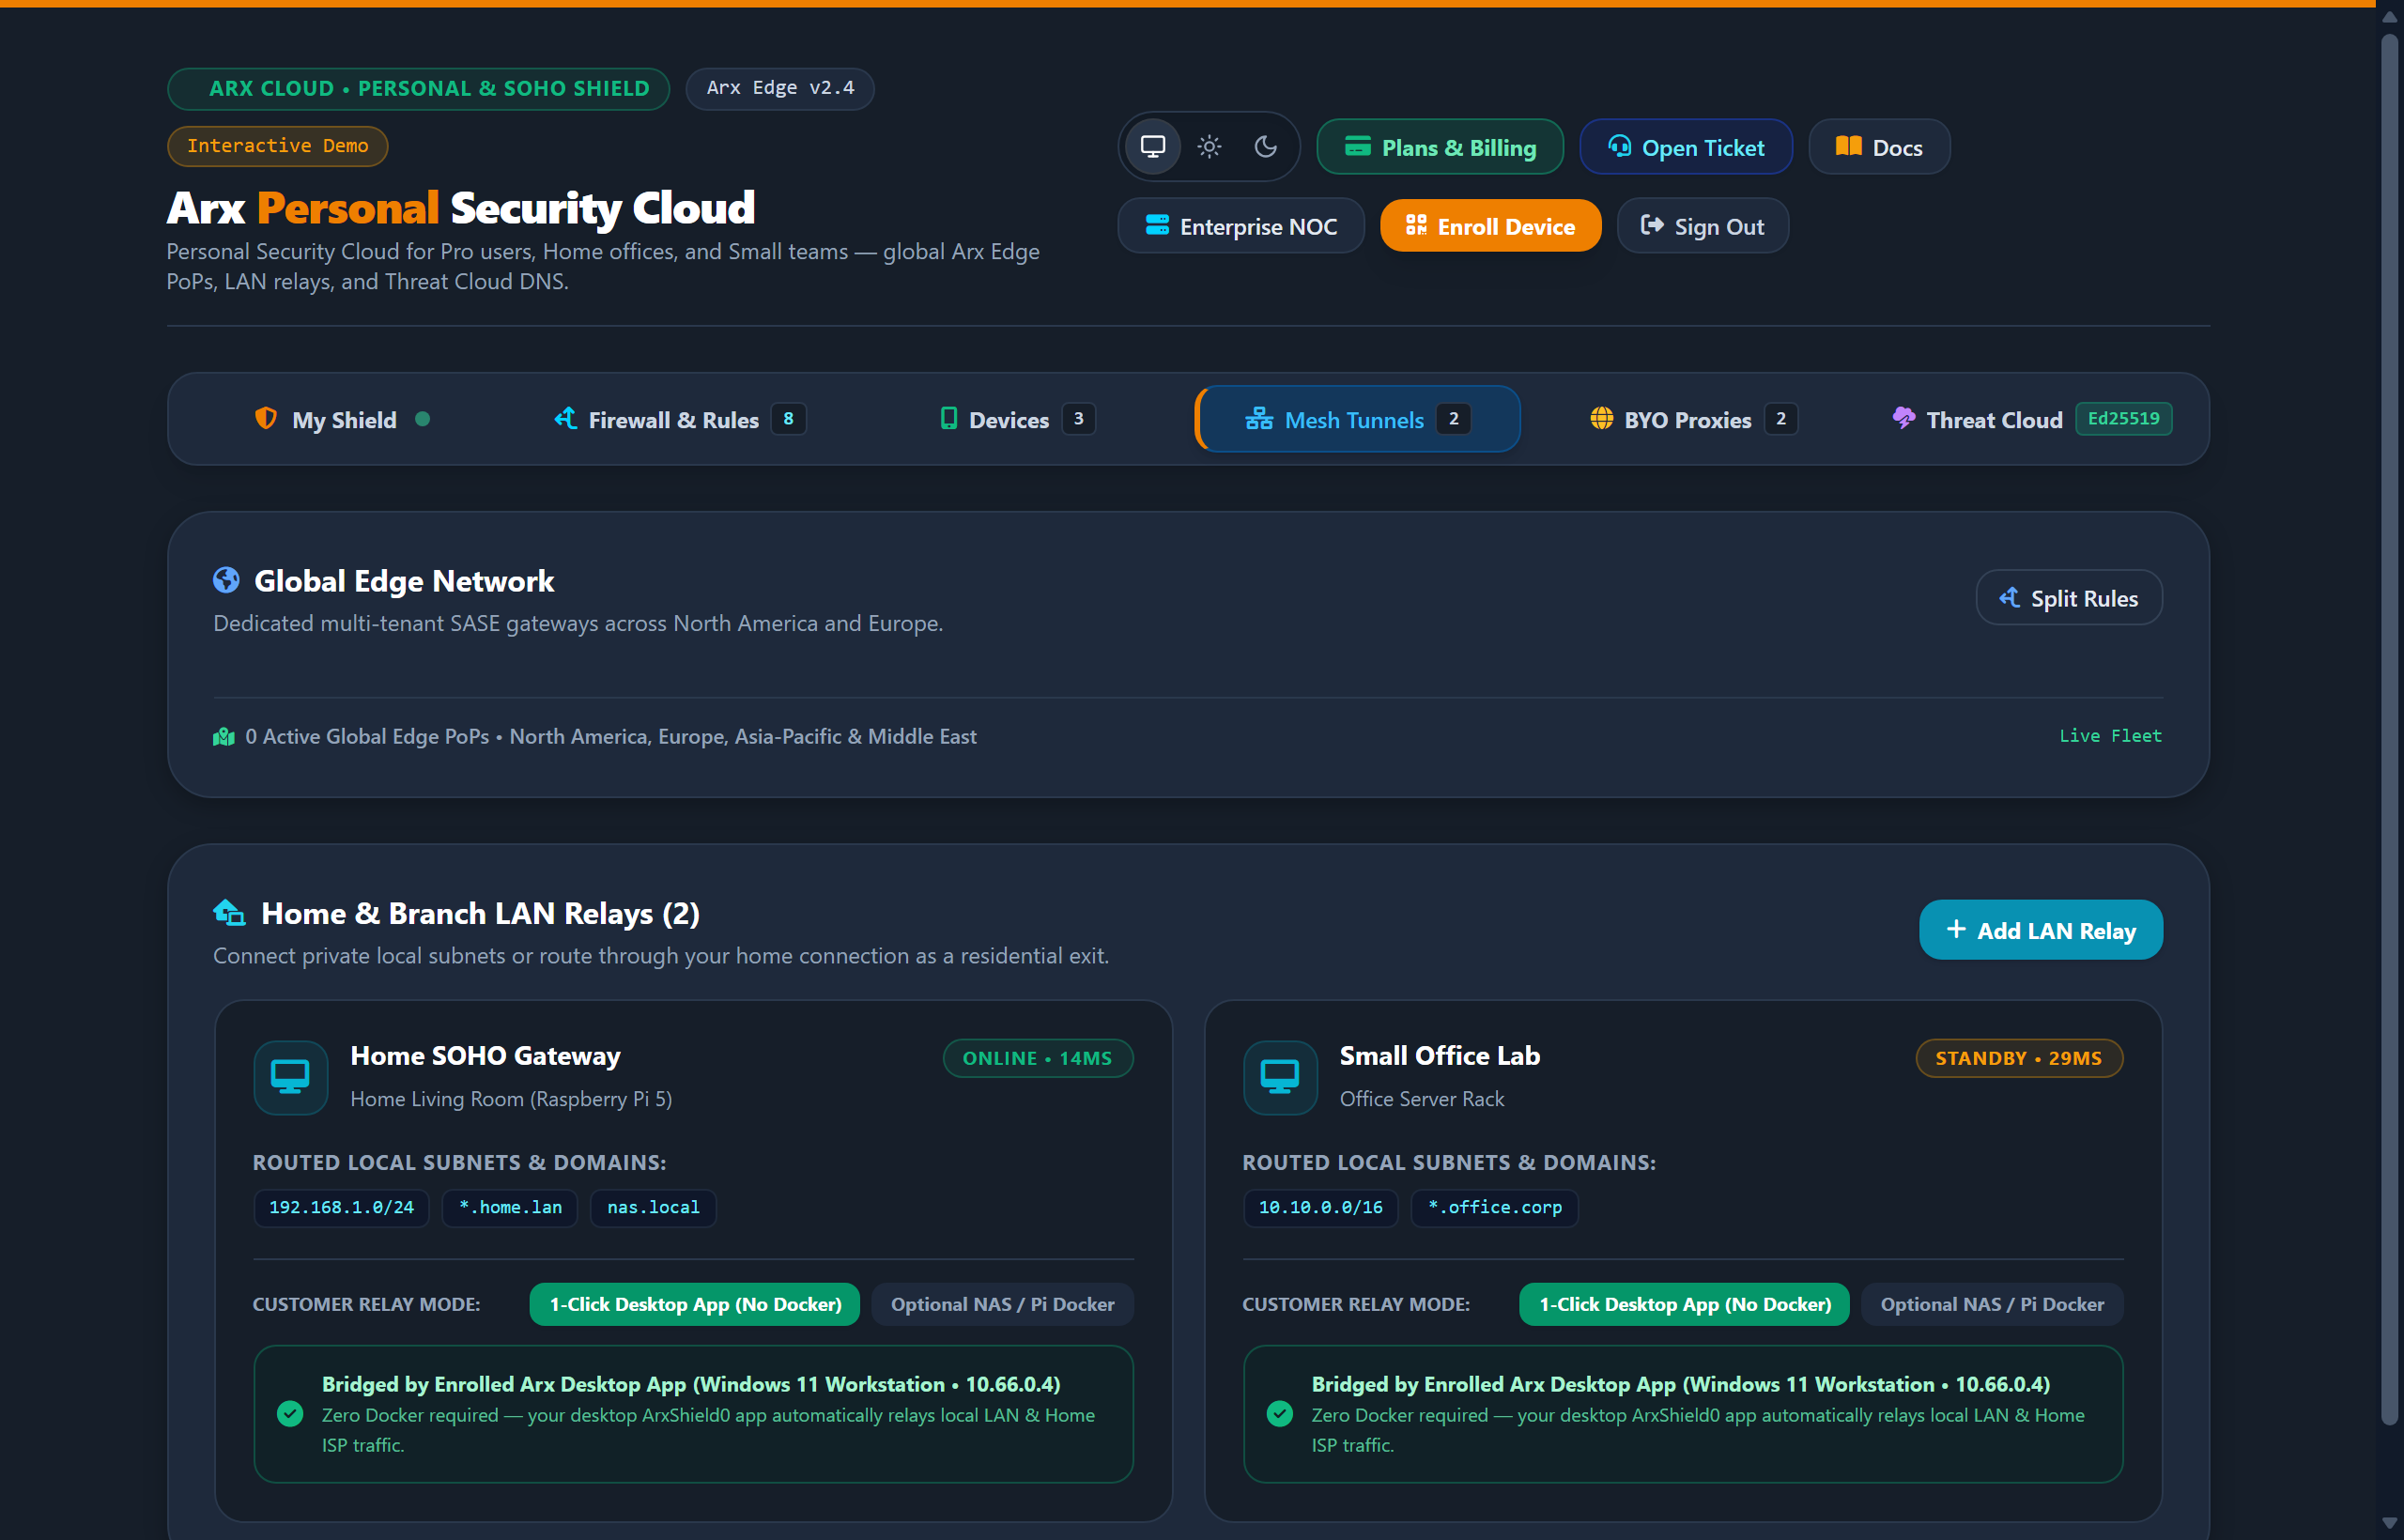
192.168.1.0/24 and nas.local via an outbound-only relay.
Personal Security Cloud FAQ
Common questions from people switching from Tailscale, ZeroTier, NordVPN, or Mullvad.
Is Arx Cloud just another Tailscale or mesh VPN?
ArxShield0 tunnel is simply the on-ramp to a single-pass Cloud Firewall, 0ms direct video breakout, AI/web DLP, 278,000+ Ed25519 Threat Cloud DNS rules, 12 global exit nodes, and zero-port home LAN relays.